Full explanation
How Source checkout works in production
Study Source checkout in the specific context of CI/CD Execution and Deployment Controls by connecting its mechanism to a production decision. First establish what owns the configuration or state, who or what invokes it, and which dependency must already be available. Then state the requirement, configure the smallest working unit, connect its dependencies, test success and failure, and document operational ownership. Relate the result to the module prerequisites and the following Dependency installation concept. The final proof is not that a command completed; it is that the intended behavior, control, and recovery path are observable and repeatable.
Purpose: provides a concrete platform capability that must be configured, secured, validated, observed, and owned throughout its lifecycle.
Dependency context: connect Source checkout in CI/CD Execution and Deployment Controls to the module prerequisites and the following Dependency installation concept.
Validation: prove intended behavior and a controlled failure path with retained evidence.
Production ownership: document who changes, observes, approves, and recovers this capability.
Flow diagram
Source checkout execution flow
A repeatable sequence for learning, implementing, validating, and operating Source checkout.
- 01FrameState the concrete problem Source checkout must solve in CI/CD Execution and Deployment Controls.
- 02InspectRead current configuration, dependencies, identity, state, and operational signals before changing anything.
- 03ImplementState the requirement, configure the smallest working unit, connect its dependencies, test success and failure, and document operational ownership.
- 04ValidateTest normal behavior, one realistic failure, and the evidence produced by Source checkout.
- 05OperateAssign ownership, monitoring, change control, and recovery guidance for the capability.
Flow diagram
CI/CD Execution and Deployment Controls module flow
See where Source checkout fits in the wider CI/CD Execution and Deployment Controls operating sequence.
- 01CheckoutCI/CD Execution and Deployment Controls stage 1: checkout with an auditable result before the next stage begins.
- 02Build and testCI/CD Execution and Deployment Controls stage 2: build and test with an auditable result before the next stage begins.
- 03Analyze and scanCI/CD Execution and Deployment Controls stage 3: analyze and scan with an auditable result before the next stage begins.
- 04Package artifactCI/CD Execution and Deployment Controls stage 4: package artifact with an auditable result before the next stage begins.
- 05Promote environmentsCI/CD Execution and Deployment Controls stage 5: promote environments with an auditable result before the next stage begins.
- 06Validate and roll backCI/CD Execution and Deployment Controls stage 6: validate and roll back with an auditable result before the next stage begins.
Official Microsoft reference
Architecture diagrams from Microsoft documentation
Use these diagrams beside the original Edukron notes and flows to compare the learning model with the official product and architecture view.
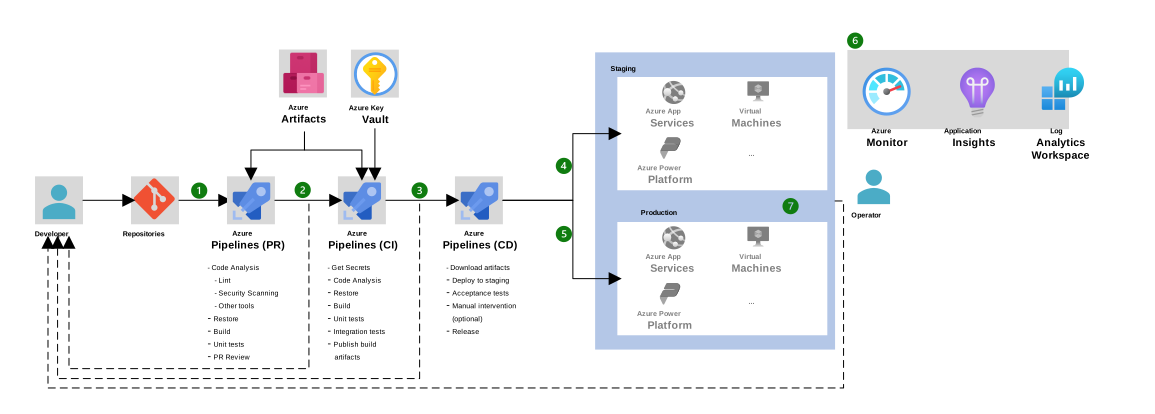
CI/CD baseline architecture with Azure Pipelines
A pull-request pipeline validates changes, CI produces a versioned artifact, CD promotes it through staging and production, and Azure observability closes the feedback loop.
Hands-on practice
Build and prove the behavior
- Create a minimal Source checkout example inside the deliver an application through four environments lab.
- Record the configuration or command, expected result, observed evidence, and one negative test.
- Explain how identity, security, monitoring, and rollback apply before treating the exercise as complete.
Production considerations
Common mistakes and control checks
Using default configuration without checking limits, identity, network access, lifecycle behavior, monitoring, or failure recovery.
Treating Source checkout as a tool feature instead of a controlled part of the end-to-end CI/CD Execution and Deployment Controls flow.
Keeping only a successful screenshot while discarding the configuration, test conditions, logs, and recovery evidence.
Knowledge check
Confirm that you can explain and apply it
01What problem does Source checkout solve, how does it work in CI/CD Execution and Deployment Controls, and what is it commonly confused with?
Define the mechanism and ownership boundary first. Explain that it provides a concrete platform capability that must be configured, secured, validated, observed, and owned throughout its lifecycle, then contrast it with the adjacent responsibilities represented by the module prerequisites and the following Dependency installation concept. Close with a concrete validation signal.
02How would you implement and validate Source checkout for a production workload?
Start from workload constraints and existing state. State the requirement, configure the smallest working unit, connect its dependencies, test success and failure, and document operational ownership. Include identity, dependencies, normal and failure tests, monitoring, and an explicit recovery decision.
03A change involving Source checkout causes a production symptom. What evidence would you inspect and how would you recover safely?
Establish scope and recent change, inspect the native configuration and event or log evidence, test the dependency boundary, apply the smallest reversible mitigation, verify user impact has recovered, and retain the findings for permanent prevention.