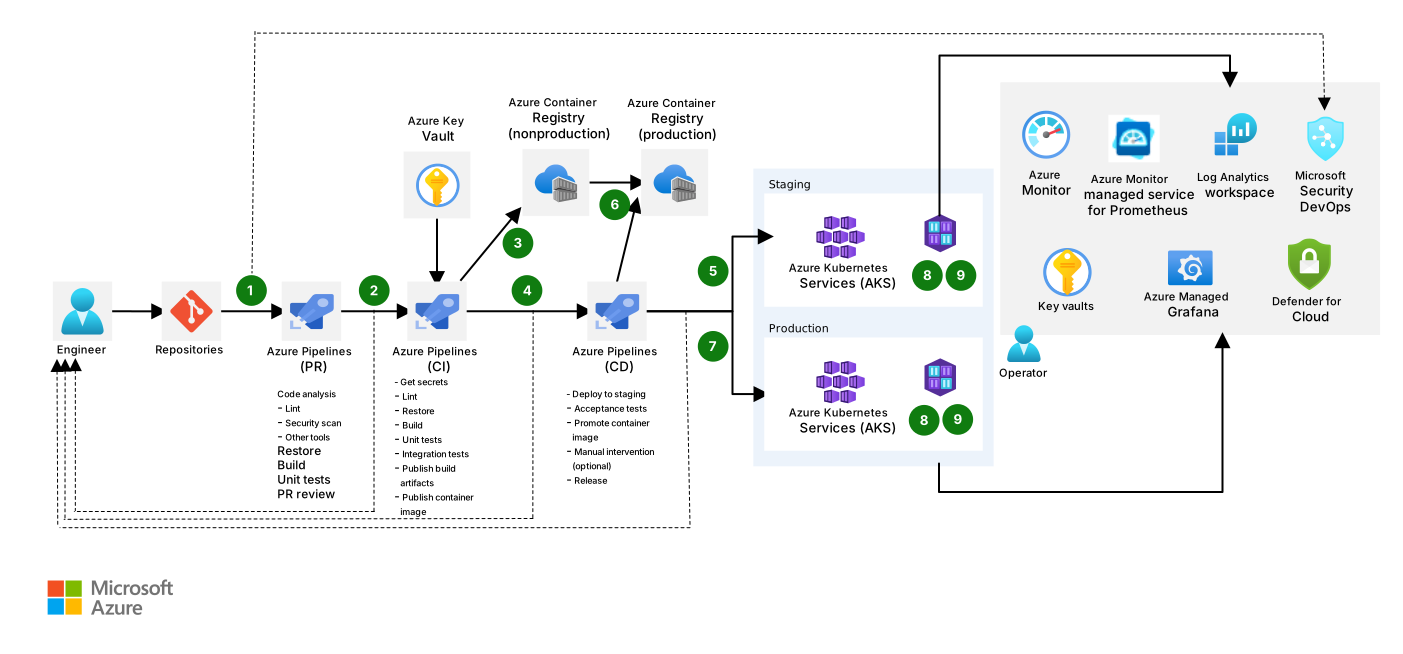
Shift-left security
Shift-left security controls which actor may perform which action on which resource, under which conditions, with evidence that can be reviewed later within DevSecOps Security Scanning. It is not an isolated definition: its value appears when it supports scan the earliest artifact that can reveal a risk, avoid relying on one tool, protect scanner credentials, tune rules with security ownership, retain reports, and treat exceptions as expiring risk decisions.
Open full notes