ContainersIntermediate10 submodules

Azure Container Registry

Operate Azure Container Registry as a private, authenticated, replicated, and scanned distribution point for versioned container images.

From concept to production evidence

Publish immutable content-addressable images from trusted pipelines, authenticate with workload identity, restrict network access, retain deliberate tags, and replicate only where latency and resilience require it.

Learning outcomes

  • Create and secure ACR
  • Organize repositories, images, and tags
  • Authenticate pipelines and runtimes
  • Push and pull through service connections
  • Use ACR Tasks and geo-replication

Azure Container Registry end-to-end flow

Use this sequence as the operating backbone for every submodule note and hands-on exercise.

  1. 01
    Build imageAzure Container Registry stage 1: build image with an auditable result before the next stage begins.
  2. 02
    Authenticate identityAzure Container Registry stage 2: authenticate identity with an auditable result before the next stage begins.
  3. 03
    Push immutable tagAzure Container Registry stage 3: push immutable tag with an auditable result before the next stage begins.
  4. 04
    Scan and retainAzure Container Registry stage 4: scan and retain with an auditable result before the next stage begins.
  5. 05
    Replicate if neededAzure Container Registry stage 5: replicate if needed with an auditable result before the next stage begins.
  6. 06
    Pull from runtimeAzure Container Registry stage 6: pull from runtime with an auditable result before the next stage begins.

Architecture diagrams from Microsoft documentation

Use these diagrams beside the original Edukron notes and flows to compare the learning model with the official product and architecture view.

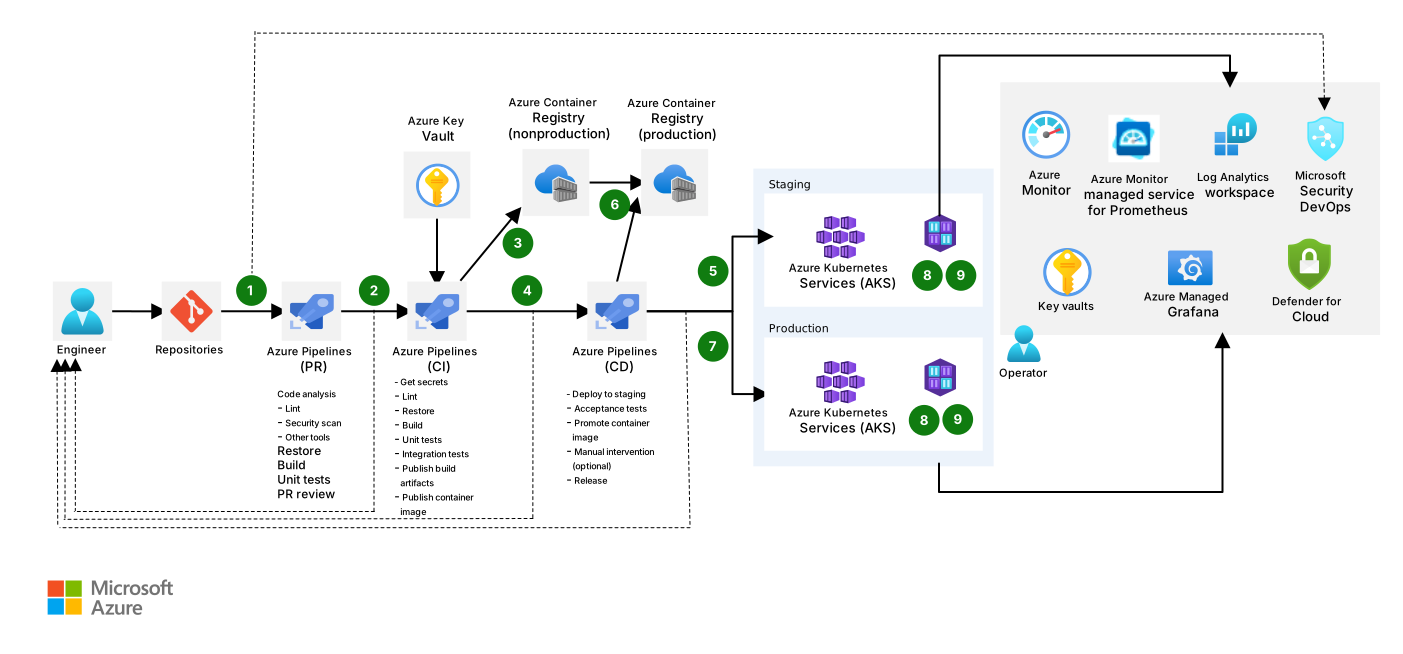
Official Microsoft architecture for building and deploying AKS applications with Azure Pipelines, ACR, security, and observability.

Azure Pipelines CI/CD architecture for AKS

The architecture connects PR validation, CI, container registries, staged AKS deployment, promotion, security scanning, Key Vault, Azure Monitor, Prometheus, Grafana, and Log Analytics.

Create a secure image supply path

  1. Create private ACR
  2. Configure workload identity or service connection
  3. Push version and digest tags
  4. Run an ACR task and scan
  5. Integrate a runtime pull and optional replica

10 full submodule notes

Read in order
01

ACR creation

ACR creation provides a concrete platform capability that must be configured, secured, validated, observed, and owned throughout its lifecycle within Azure Container Registry. It is not an isolated definition: its value appears when it supports publish immutable content-addressable images from trusted pipelines, authenticate with workload identity, restrict network access, retain deliberate tags, and replicate only where latency and resilience require it.

Open full notes
02

Repositories

Repositories provides a concrete platform capability that must be configured, secured, validated, observed, and owned throughout its lifecycle within Azure Container Registry. It is not an isolated definition: its value appears when it supports publish immutable content-addressable images from trusted pipelines, authenticate with workload identity, restrict network access, retain deliberate tags, and replicate only where latency and resilience require it.

Open full notes
03

Images

Images moves a versioned change toward users through repeatable validation, immutable artifacts, controlled promotion, and recoverable release decisions within Azure Container Registry. It is not an isolated definition: its value appears when it supports publish immutable content-addressable images from trusted pipelines, authenticate with workload identity, restrict network access, retain deliberate tags, and replicate only where latency and resilience require it.

Open full notes
04

Tags

Tags provides a concrete platform capability that must be configured, secured, validated, observed, and owned throughout its lifecycle within Azure Container Registry. It is not an isolated definition: its value appears when it supports publish immutable content-addressable images from trusted pipelines, authenticate with workload identity, restrict network access, retain deliberate tags, and replicate only where latency and resilience require it.

Open full notes
05

Authentication

Authentication controls which actor may perform which action on which resource, under which conditions, with evidence that can be reviewed later within Azure Container Registry. It is not an isolated definition: its value appears when it supports publish immutable content-addressable images from trusted pipelines, authenticate with workload identity, restrict network access, retain deliberate tags, and replicate only where latency and resilience require it.

Open full notes
06

Service connections

Service connections provides a concrete platform capability that must be configured, secured, validated, observed, and owned throughout its lifecycle within Azure Container Registry. It is not an isolated definition: its value appears when it supports publish immutable content-addressable images from trusted pipelines, authenticate with workload identity, restrict network access, retain deliberate tags, and replicate only where latency and resilience require it.

Open full notes
07

Image push/pull

Image push/pull moves a versioned change toward users through repeatable validation, immutable artifacts, controlled promotion, and recoverable release decisions within Azure Container Registry. It is not an isolated definition: its value appears when it supports publish immutable content-addressable images from trusted pipelines, authenticate with workload identity, restrict network access, retain deliberate tags, and replicate only where latency and resilience require it.

Open full notes
08

ACR Tasks

ACR Tasks provides a concrete platform capability that must be configured, secured, validated, observed, and owned throughout its lifecycle within Azure Container Registry. It is not an isolated definition: its value appears when it supports publish immutable content-addressable images from trusted pipelines, authenticate with workload identity, restrict network access, retain deliberate tags, and replicate only where latency and resilience require it.

Open full notes
09

Geo-replication

Geo-replication preserves durable information with explicit ownership, consistency, access, lifecycle, replication, and recovery guarantees within Azure Container Registry. It is not an isolated definition: its value appears when it supports publish immutable content-addressable images from trusted pipelines, authenticate with workload identity, restrict network access, retain deliberate tags, and replicate only where latency and resilience require it.

Open full notes
10

ACR security

ACR security controls which actor may perform which action on which resource, under which conditions, with evidence that can be reviewed later within Azure Container Registry. It is not an isolated definition: its value appears when it supports publish immutable content-addressable images from trusted pipelines, authenticate with workload identity, restrict network access, retain deliberate tags, and replicate only where latency and resilience require it.

Open full notes