Shift-left security
Concept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setGood answers place each test at the right lifecycle stage, explain signal and limitations, reduce noise, protect reports, and use severity, exploitability, and exposure in gate decisions.
Interview focus
Good answers place each test at the right lifecycle stage, explain signal and limitations, reduce noise, protect reports, and use severity, exploitability, and exposure in gate decisions.
Flow diagram
Use this flow to structure design and scenario answers from context through evidence and recovery.
Official Microsoft reference
Use these diagrams beside the original Edukron notes and flows to compare the learning model with the official product and architecture view.
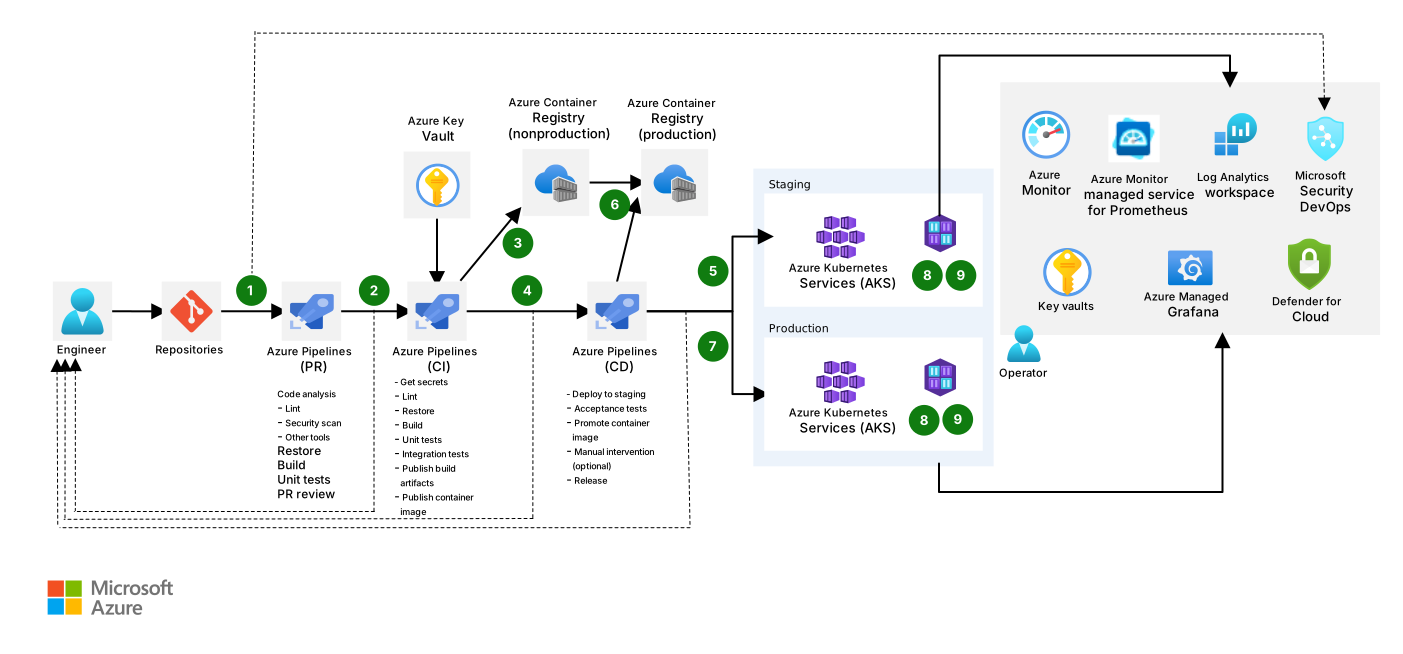
The architecture connects PR validation, CI, container registries, staged AKS deployment, promotion, security scanning, Key Vault, Azure Monitor, Prometheus, Grafana, and Log Analytics.
Practical interview scenario
A release pipeline runs only a nightly SAST scan and high-severity findings are emailed after production. Redesign the security path across source, dependencies, infrastructure, images, and a live test environment.
Module question spotlight
Define the mechanism and ownership boundary first. Explain that it controls which actor may perform which action on which resource, under which conditions, with evidence that can be reviewed later, then contrast it with the adjacent responsibilities represented by the module prerequisites and the following SAST concept. Close with a concrete validation signal.
Start from workload constraints and existing state. State the requirement, configure the smallest working unit, connect its dependencies, test success and failure, and document operational ownership. Include identity, dependencies, normal and failure tests, monitoring, and an explicit recovery decision.
Establish scope and recent change, inspect the native configuration and event or log evidence, test the dependency boundary, apply the smallest reversible mitigation, verify user impact has recovered, and retain the findings for permanent prevention.
Define the mechanism and ownership boundary first. Explain that it provides a concrete platform capability that must be configured, secured, validated, observed, and owned throughout its lifecycle, then contrast it with the adjacent responsibilities represented by the preceding DAST concept and the following Secret scanning concept. Close with a concrete validation signal.
Start from workload constraints and existing state. Identify the actor, authentication method, permission scope, protected resource, expiry or rotation behavior, and audit event. Include identity, dependencies, normal and failure tests, monitoring, and an explicit recovery decision.
Complete question bank
Concept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question setConcept, implementation, and troubleshooting questions with model answers, evaluation points, follow-ups, and weak-answer warnings.
Open question set